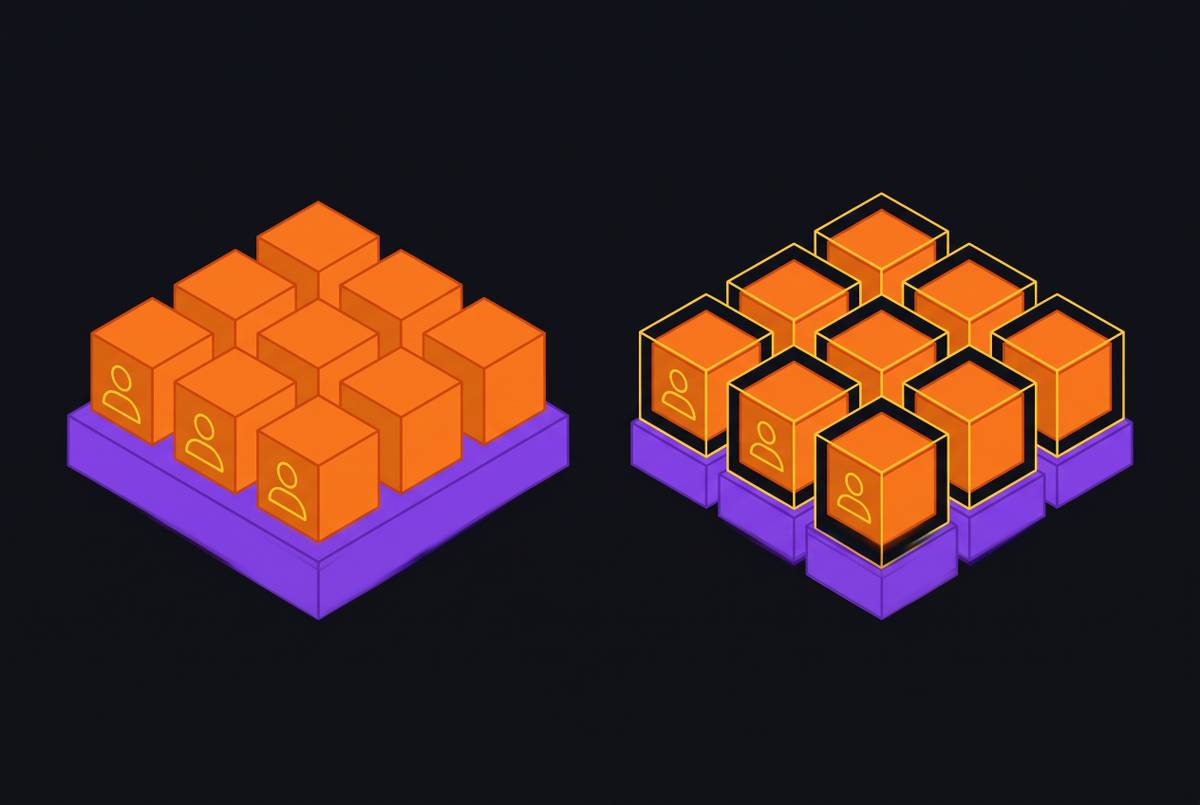
Container Isolation vs Micro-VM Isolation for Agent Sandboxing
Kernel boundaries matter more than startup speed when sandboxing untrusted agent-generated code.
Tobias Wrenfield
Senior Contributor
Tobias has been writing about systems security and sandboxing since the container-security debates of the mid-2010s, drawing on an earlier career in penetration testing and threat modeling. His work focuses on the boundaries between isolation guarantees and practical developer workflows.
1 story
Kernel boundaries matter more than startup speed when sandboxing untrusted agent-generated code.