Swapping the Container Runtime for a Firecracker Kernel per Agent
Firecracker microVMs give untrusted agent code its own kernel and hardware-enforced isolation.
Priya Subramaniam
Section
9 stories in Micro-VM Infrastructure.
Firecracker microVMs give untrusted agent code its own kernel and hardware-enforced isolation.
Bare metal and careful tuning unlock production-scale Firecracker for AI agents.
Firecracker's hardware-isolated kernels let AI agents install packages and customize systems safely.
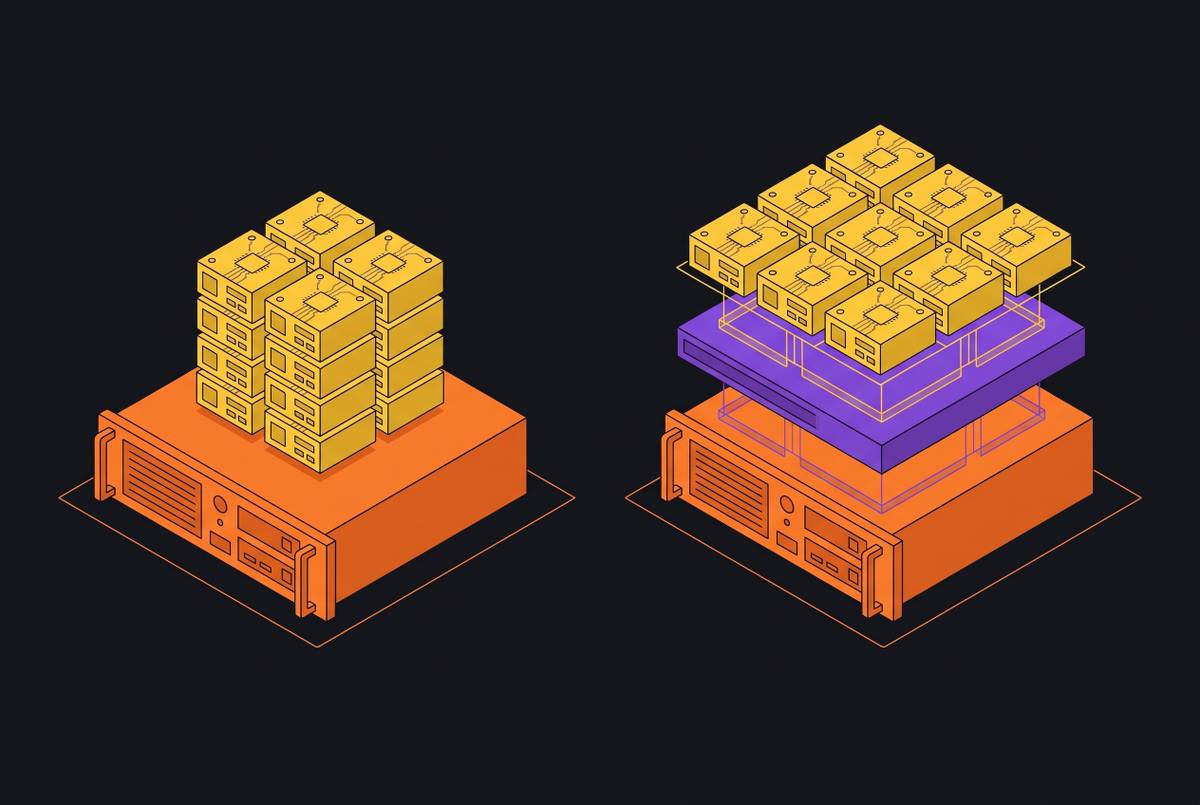
Bare metal hosts deliver faster snapshots and denser agent fleets than nested virtualization.
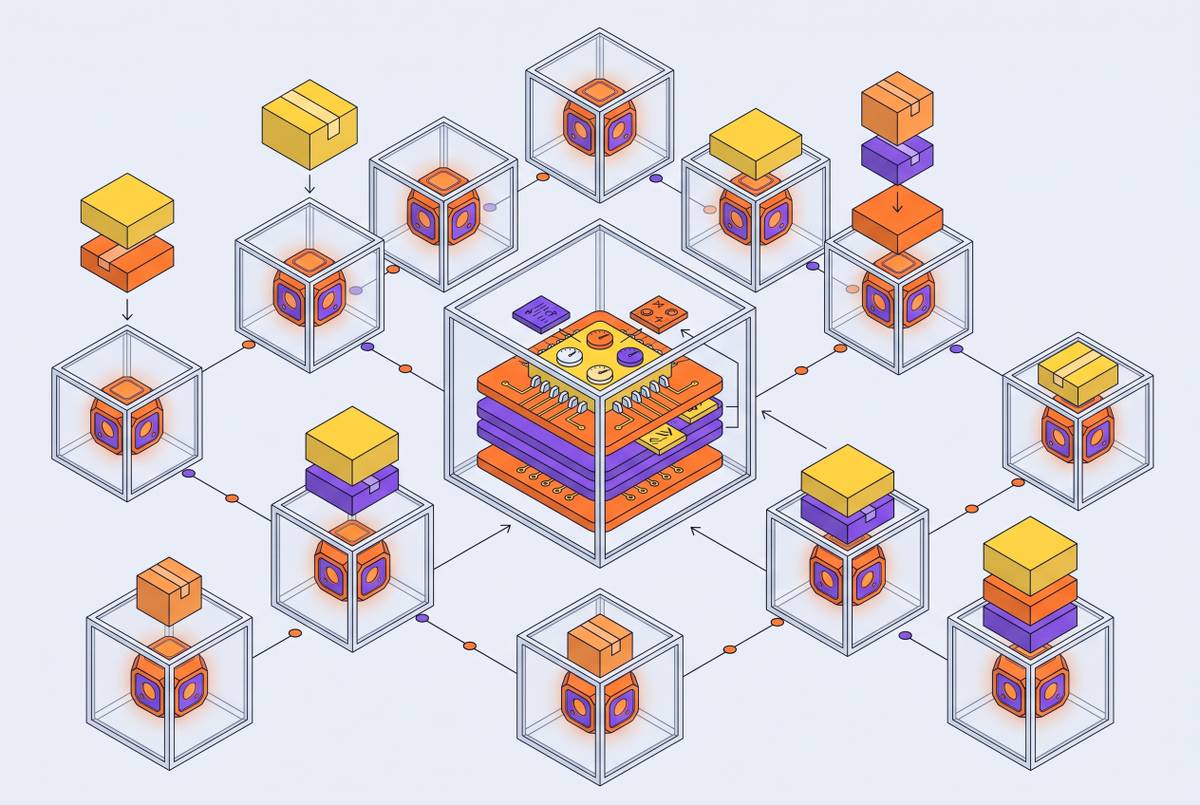
Firecracker isolates AI agents in separate kernels to contain untrusted code.
Firecracker's fast, lightweight microVMs make per-agent kernel isolation practical.
Isolating an agent's compute is not enough without host-enforced egress.
Containers share the host kernel; microVMs give each agent its own.